Stage 01 — Design advisory
Before code is written.
Reviewing protocol architecture, threat models, and economic design while choices are still cheap to change.
01 / AI-native cybersecurity
We work with your team from design through post-deployment. Our auditors review, fuzz, and scan with AI in the loop.
Nearly half of all audits discover at least one critical or high severity issue — 114 of 237.
38 critical or high findings with the ack3 AI scan, 31 without — backtest on 2025 production audits.
Blue chips such as Lido run the ack3 AI scan: one review that combines on-chain contracts and off-chain infrastructure.
What impressed us most was the AI audit's ability to identify complex issues arising from interactions between different parts of the system. These cross-component findings are typically among the most difficult classes of vulnerabilities to discover.
What we do · the partnership
The core engagement is a security review: manual review, Wake fuzzing, and the ack3 AI scan across EVM smart contracts, Solana programs, and the off-chain infrastructure around them. Around the review, the partnership spans the whole lifecycle.
Stage 01 — Design advisory
Reviewing protocol architecture, threat models, and economic design while choices are still cheap to change.
Stage 02 — Tooling
We create manually guided fuzzing campaigns and run the ack3 AI scan against the codebase.
Stage 03 — Security review
A smart contract audit extends into libraries, off-chain components and dependencies that affect the system's security. Critical code stays inside the audit scope.
94.4% of losses at audited projects were outside audit scope — H1 2026 researchStage 04 — Partnership
A monthly ack3 AI scan follows the code; re-reviews and incident support as the protocol evolves — where the relationship compounds.
How we review · methodology
Every review starts with a model of the system and ends with a report the team stands behind.
The codebase and its external interactions mapped; expected behavior checked against implementation.
wake graph tooling · mathematical modelsLaunched at the start, pinned to the scoped commit, run in parallel with the manual review — added coverage and leads, every finding reviewed by the team.
scoped commit · manual triageVulnerability hypotheses, escalation paths, chained weaknesses, trust boundaries — every finding validated by auditors.
ai workflows · wake static analyzer · lspUnit tests and fuzzing confirm findings and verify exact behavior — campaigns guided by an auditor, fuzz tests AI-generated.
wake test · fuzz campaignsThe team
ack3 is an in-house team of security researchers — the team that built Ackee Blockchain — auditing Ethereum and Solana protocols since 2021, trusted by Lido, Safe, and Axelar. The team teaches blockchain security at the Czech Technical University in Prague, led by founder Josef Gattermayer, Ph.D.
Open source · tooling
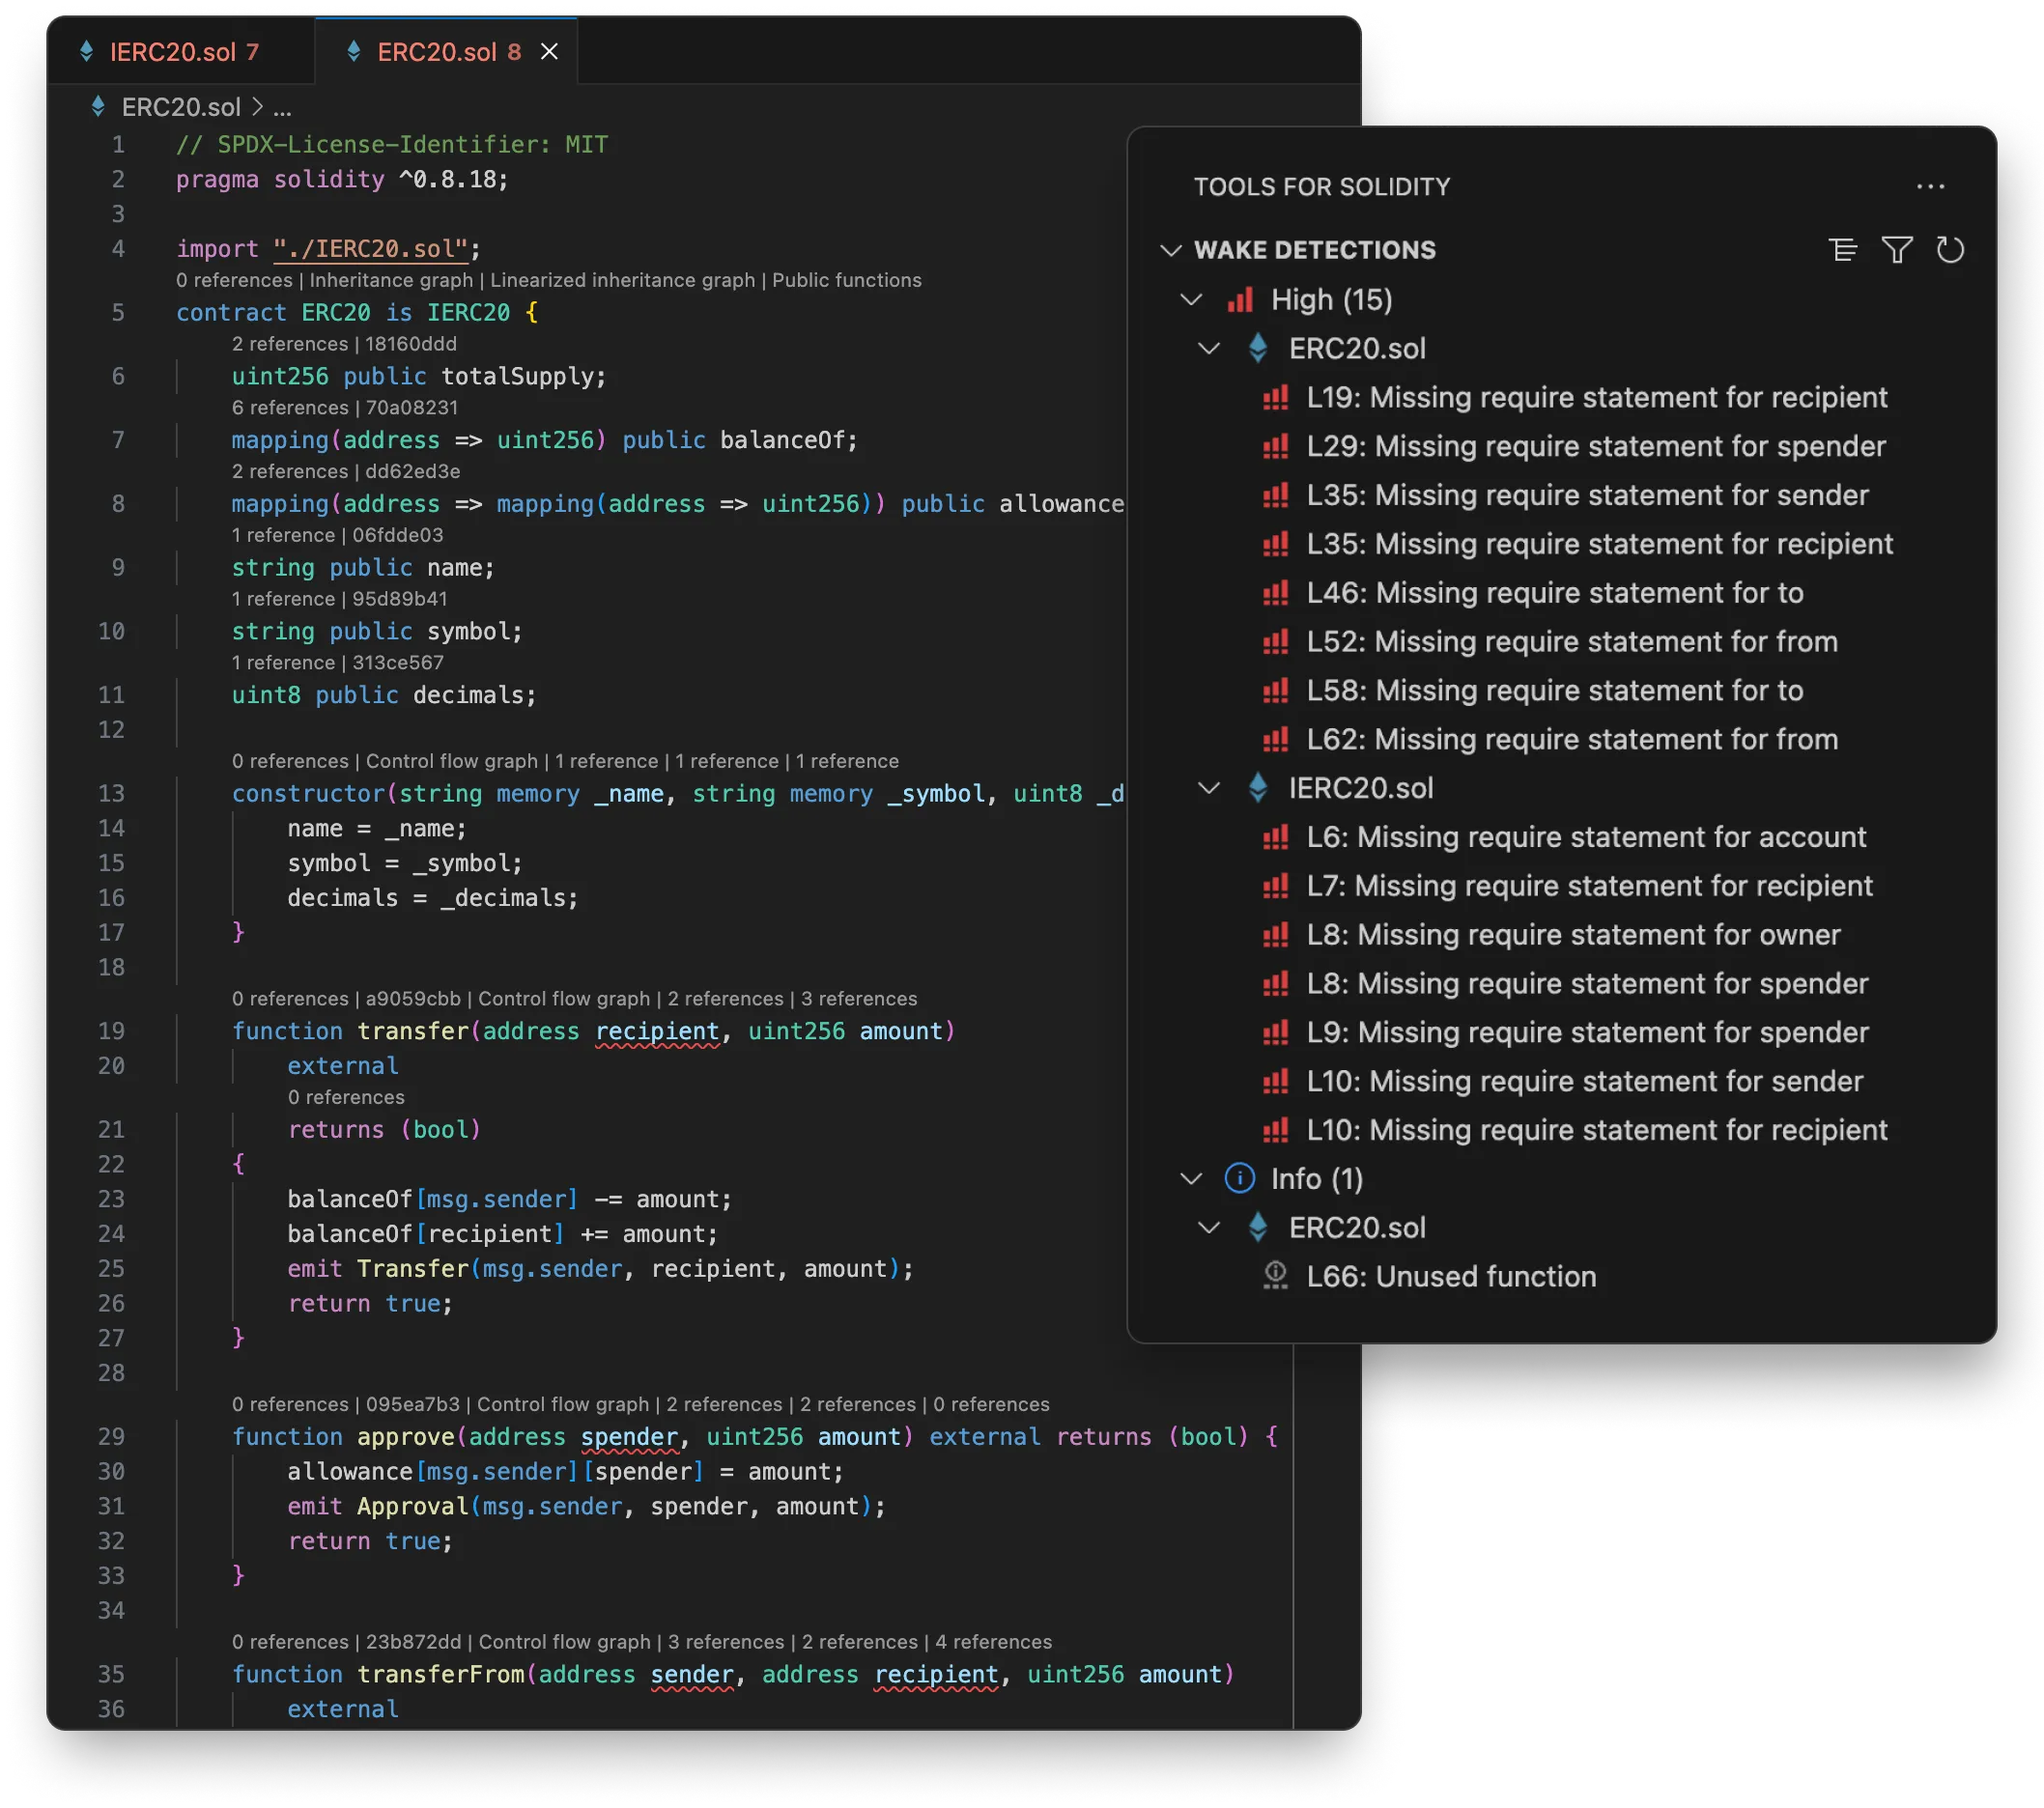
Wake is the framework behind every ack3 audit — pytest-based testing, property-based fuzzing, vulnerability detectors, and the language server that powers the Solidity (Wake) VS Code extension. It started in 2022 as the team's internal framework at Ackee Blockchain; we re-build it now for our own engagements and share it with everyone, open source.
Wake is built for the AI era: the agents drive Wake; our auditors drive the agents. The research behind it is conducted with the Czech Technical University in Prague.