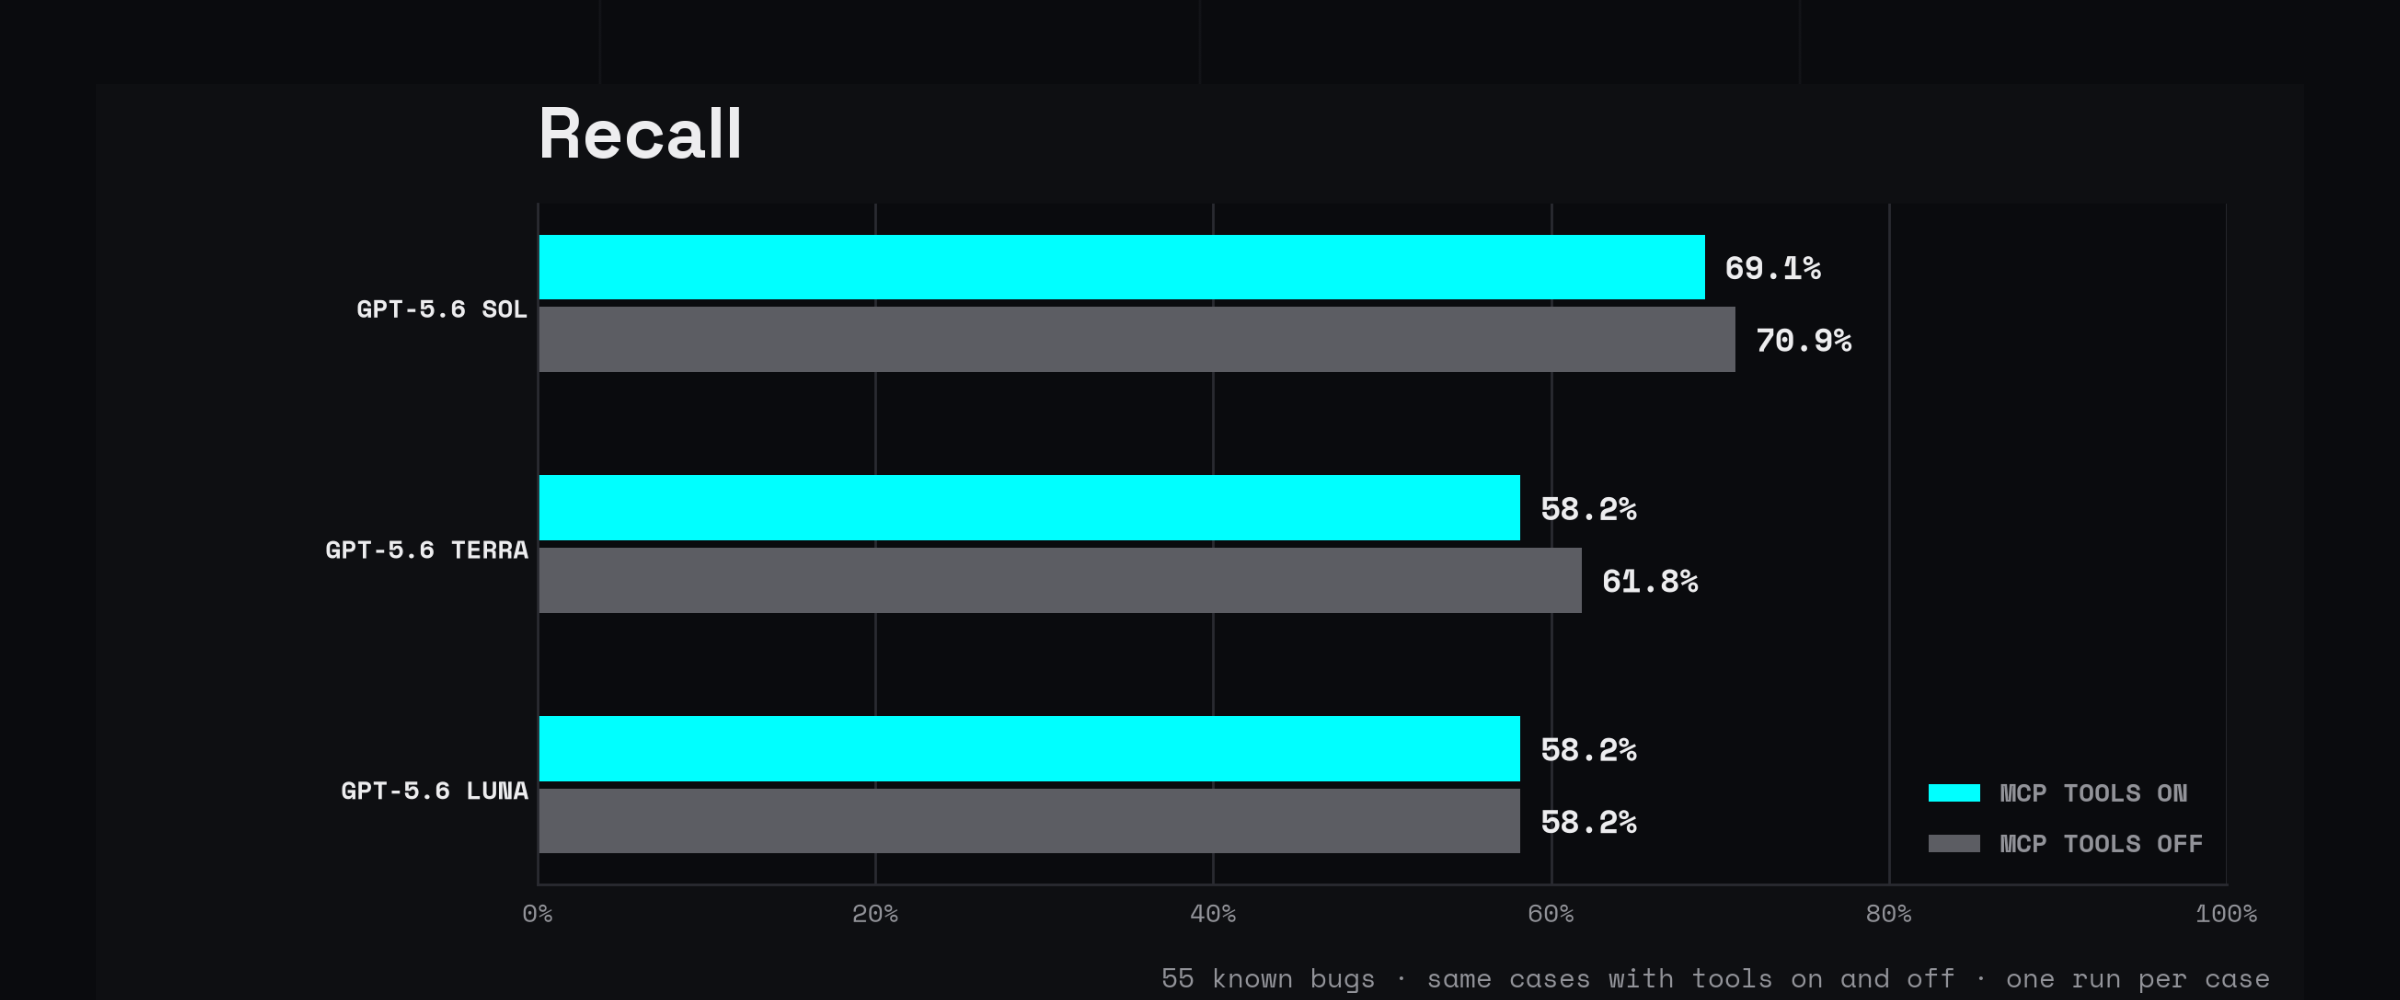
Can deterministic static-analysis MCP tools improve audit results from non-deterministic AI? Three GPT-5.6 models reviewed the same Go codebase with and without them.
Glossary definition
Security code review is the manual examination of source code and system interactions to identify defects, unsafe assumptions, and exploitable behavior.
Code review is a software quality-assurance activity in which one or several people manually review source code.
In our audits, we carefully study the codebase line by line, often several times, to reach the following goals:
Used in context
Can deterministic static-analysis MCP tools improve audit results from non-deterministic AI? Three GPT-5.6 models reviewed the same Go codebase with and without them.
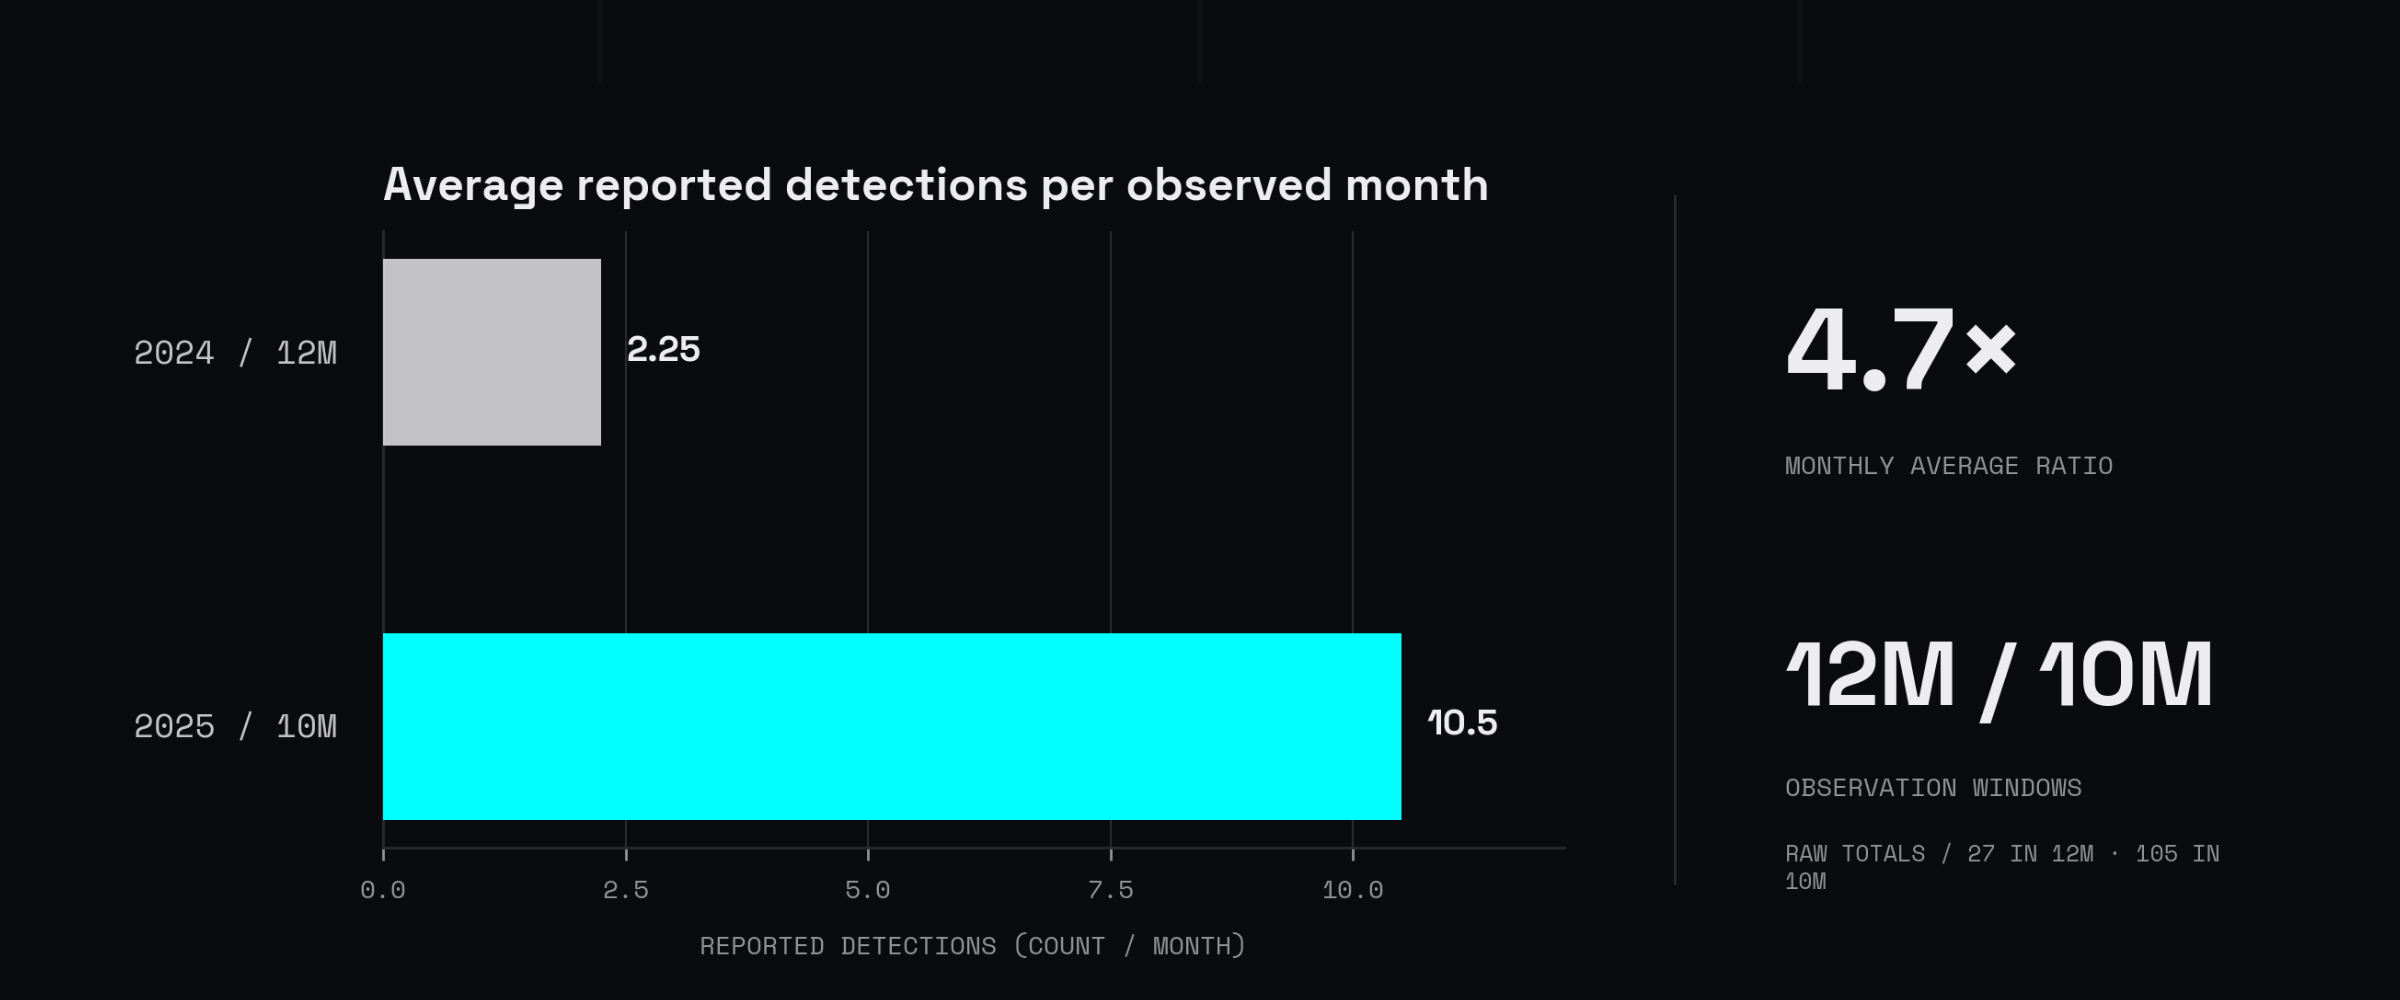
VS Code extensions run with your permissions while installs and badges are weak trust signals. Learn how to audit, pin, allowlist, and contain them.